
How it Works
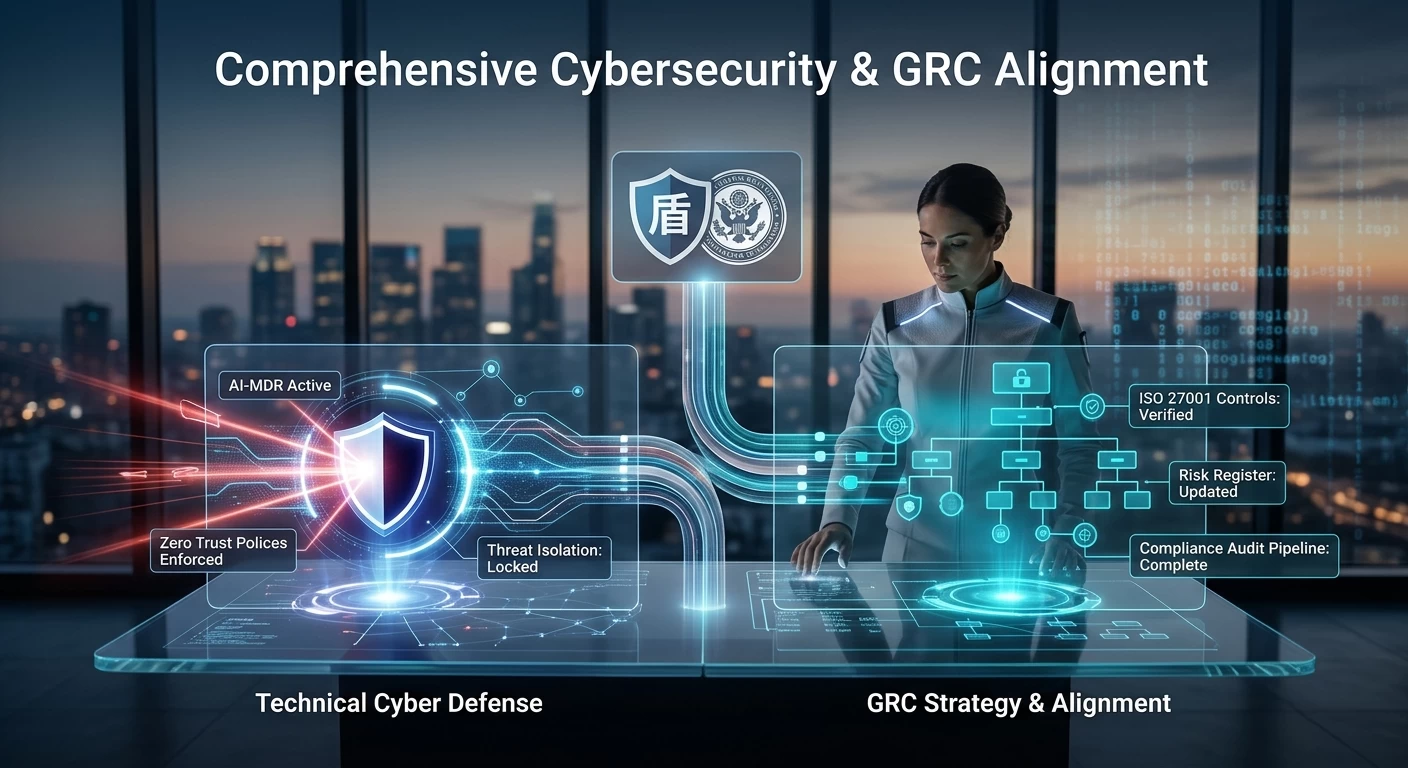
As cyber threats grow more sophisticated and regulatory environments tighten worldwide, separating technical defenses from corporate strategy is no longer viable. InfoTech Technologies delivers a unified Cyber GRC (Governance, Risk, and Compliance) and Security Operations framework that bridges the gap between deep technical protection and executive accountability. We transform security from an unpredictable operational expense into a measurable business enabler.
- The Borderless Attack Surface: With remote workforces and widespread SaaS application adoption, standard corporate network perimeters no longer exist.
- Regulatory Penalty Exposure: Regulatory bodies globally enforce massive financial and legal penalties for data breaches due to poor security practices.
- Supply Chain Trust Deadlocks: Enterprise clients increasingly refuse to sign vendor contracts unless you can provide verifiable proof of an advanced security posture (such as an ISO 27001 certificate or a SOC 2 audit report).
- AI-Driven Threat Detection and Isolation (MDR/EDR): We deploy continuous, 24/7 endpoint monitoring powered by behavioral AI. Our Managed Security Operations Center (SOC) actively hunts for anomalies, instantly isolating threats like ransomware before they spread across your network.
- Zero Trust Architecture (ZTNA): We eliminate high-risk, legacy corporate VPNs. By enforcing context-aware, identity-based access controls paired with phishing-resistant Multi-Factor Authentication (MFA), we ensure only authorized users on healthy devices can touch sensitive data assets.
- Risk-Based Vulnerability and Attack Surface Management: We continuously scan your public-facing and internal digital architecture to discover exposed systems and unpatched software flaws, prioritizing remediation based on real-world threat intelligence.
- Governance and Compliance Roadmap Implementation: We assess your operational workflows against frameworks like ISO 27001, SOC 2, or the Essential Eight. Our team builds your internal policies, risk registers, and automated log collection pipelines to assemble the definitive audit evidence required for formal certification.
- 100% Audit Readiness and Compliance Assurance: Eradicate panic before annual security assessments with continuous, automated compliance tracking and up-to-date policy documentation.
- Accelerated Enterprise Deal Velocity: Instantly answer complex security questionnaires and confidently present verified data protection certificates to win tier-one corporate and government contracts.
- Drastic Risk Exposure Reduction: Shift your business from a reactive state of recovering from breaches to a proactive model that detects and blocks unauthorized entry points before an exploit occurs.
Comprehensive IT Solutions For Modern Businesses
We are Trusted 15+ Countries Worldwide

Kiddies World
IT Operations Manager
Reliable, innovative, and highly professional. InfoTech Technologies understands our business requirements and consistently delivers technology solutions that exceed expectations.
SoftTech
Operations Manager
The team at InfoTech Technologies is responsive, knowledgeable, and always willing to go the extra mile. Their managed IT services...
Moonkle LTD
Client of Company
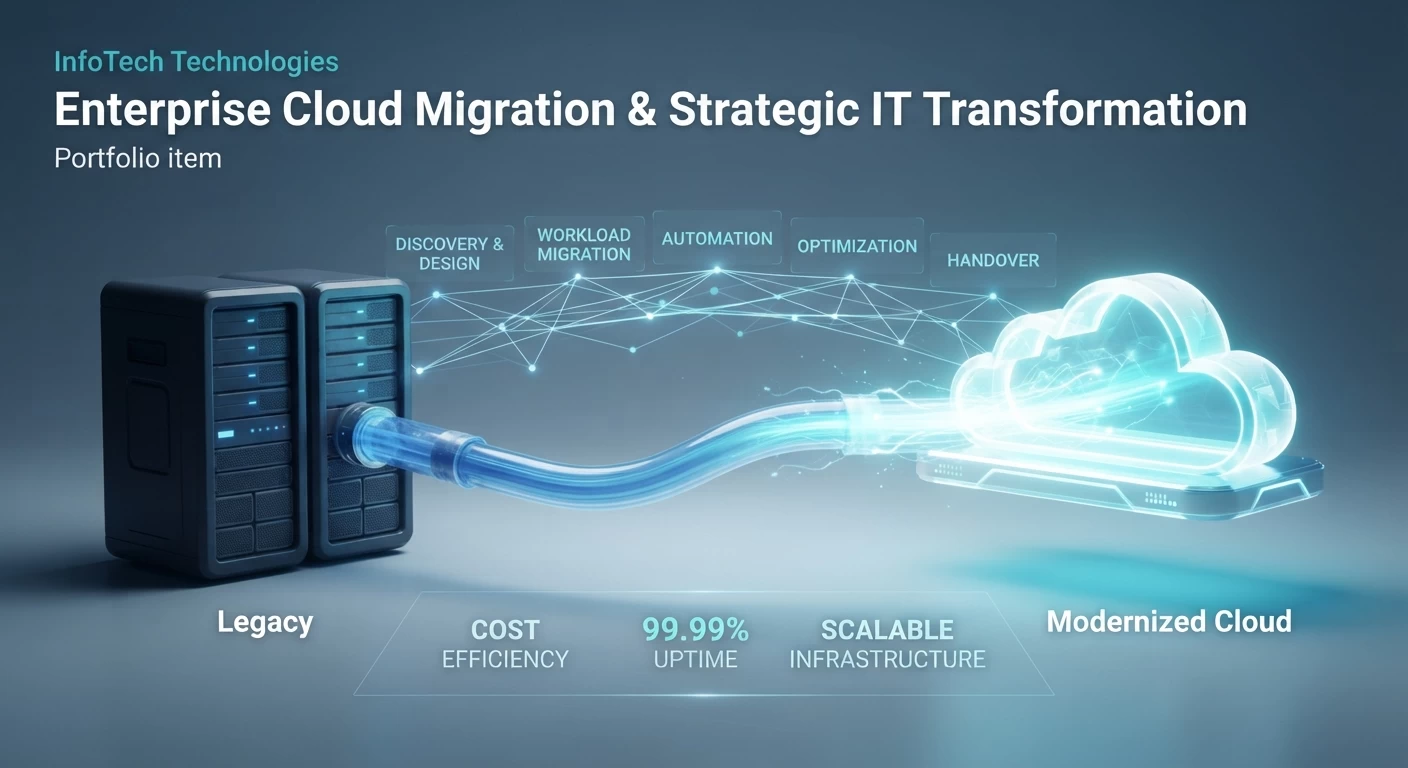
InfoTech Technologies helped modernise our entire IT infrastructure. Their team delivered a seamless cloud migration with zero disruption to our...